See every agent. Control every action.
Monitor everything your AI agents do, govern how they're used, and secure the environments they run in — right at the source.
The Layer Underneath Your Agents
Qpoint gives you a live inventory, full visibility, and policy-based controls for every agent and harness across your environments. Enforcement happens right where the agent runs, with plugins that you can run out of the box or extend to fit how your company works.
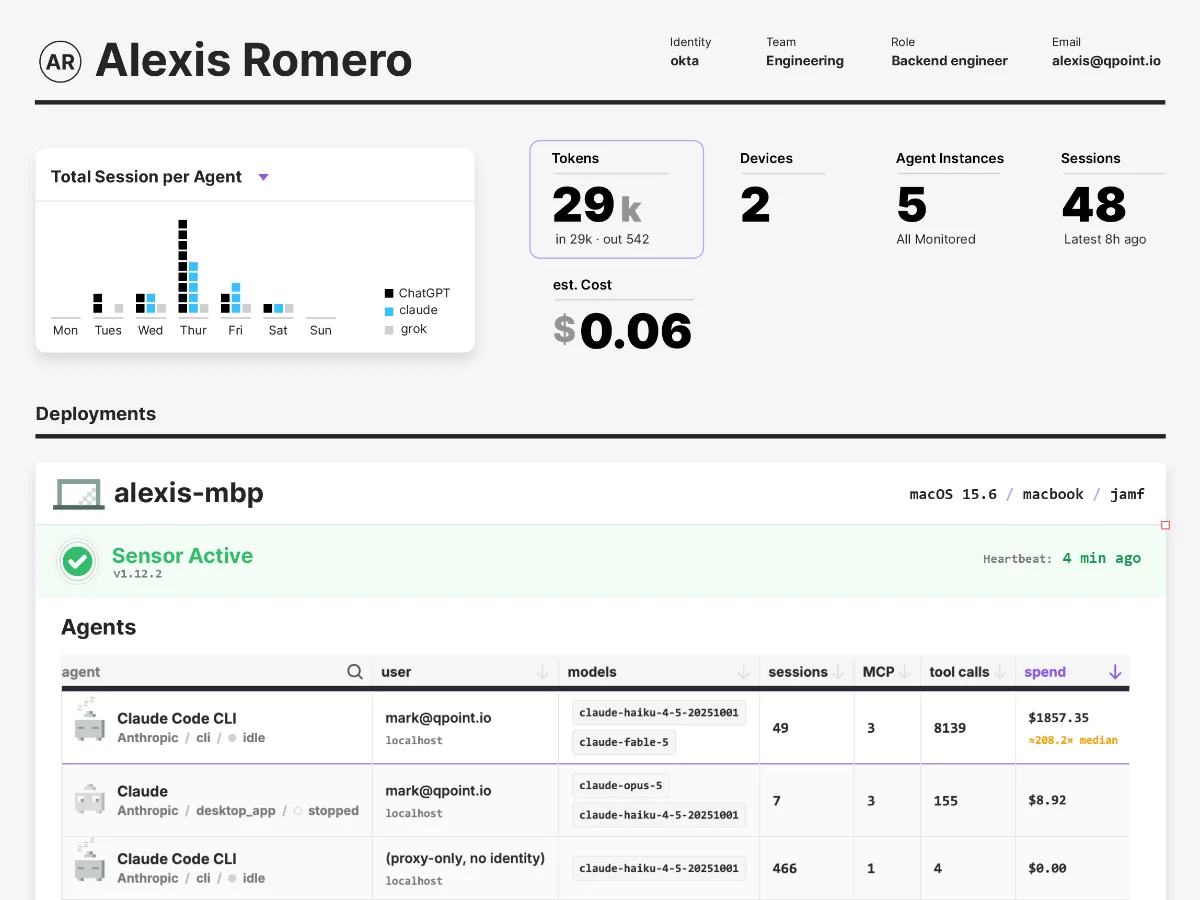
Discover every agent, everywhere, and monitor everything they do
- Keep a live inventory of every agent on endpoints and in hosted environments, regardless of runtime, framework, or harness
- Stream every file, tool call, MCP route, and outbound request as it happens
- Attribute every action to the agent and session behind it
- Export everything to your existing observability stack
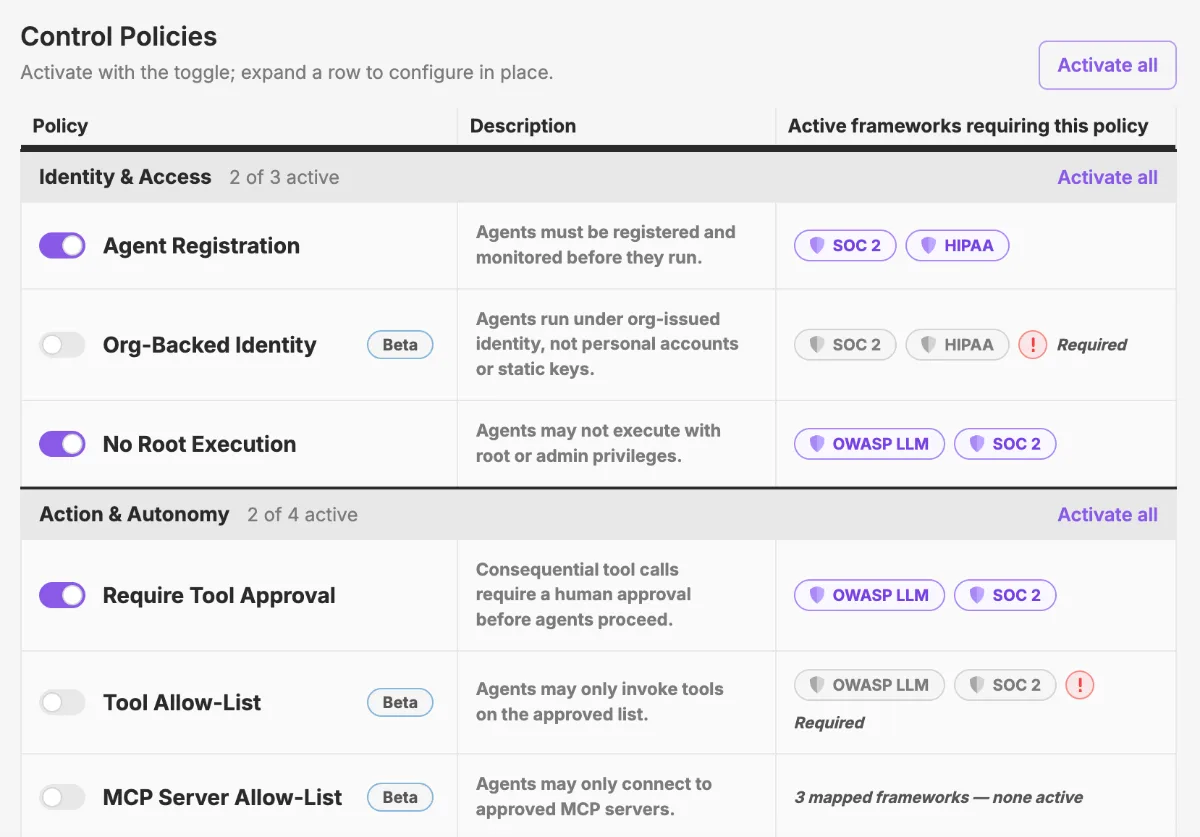
Set rules for how agents can be used and push them out to all endpoints
- Approve the MCP servers and tools that agents can use
- Define what's off limits, and apply it across every endpoint
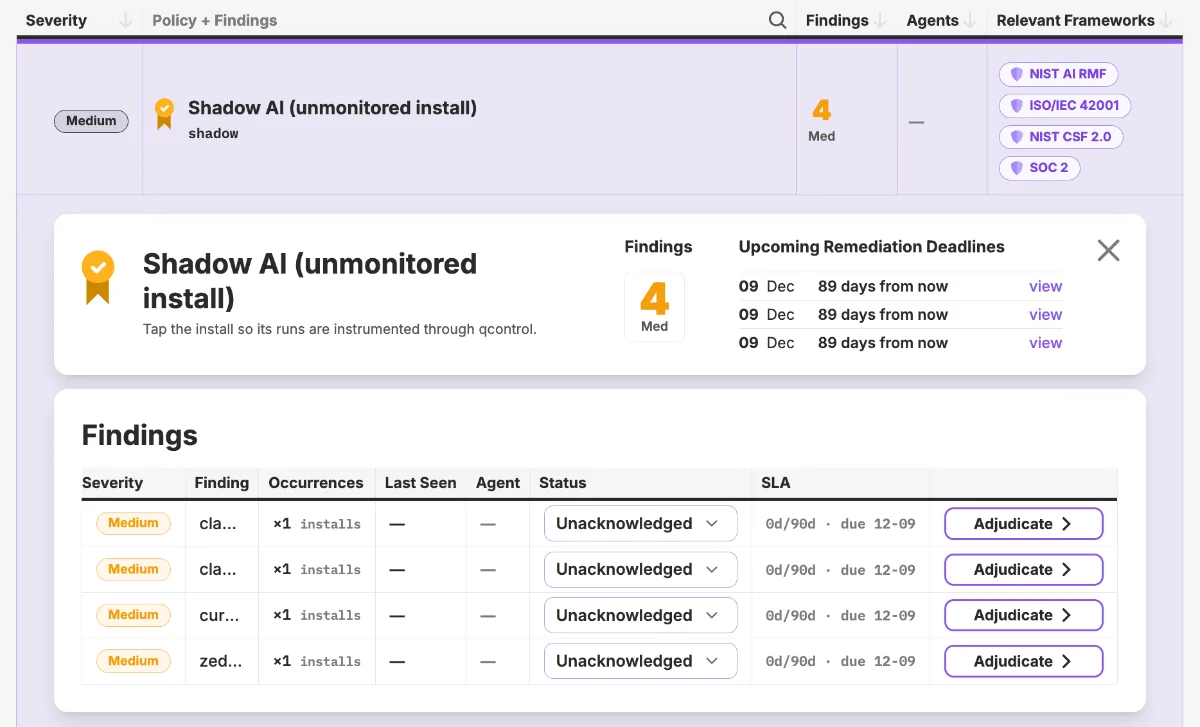
- Surface policy violations with the agent and session attached
- Monitor if you are in compliance with your own policies
Enforce policies in the agent's execution path, before the action completes
- Block reads of secrets
- Refuse unapproved endpoints
- Redact content on the way out
- Deny unapproved tool calls
Policies are plugins. Run the built-in plugins or write your own against the same hooks.
Agent visibility and control for every team
Whether you're rolling agents out, running security, or accountable for it, Qpoint meets you where you are.
IT Operations
You need to know what's running on managed devices. With agents, you also need to know what they're doing — the files they touch, the tools they call, the servers they connect to. Qpoint gives you both, without changing how anyone works.
Security Teams
Your existing tools have no concept of an agent. Qpoint operates in the agent's execution path, which gives it a unique observation point, keeps every action attributed, and applies policy at the source.
CISOs
You are accountable for what agents are doing, but you're being asked to speed up adoption at the same time. Qpoint enables rapid adoption across the organization because you can see what agents do and prevent what they shouldn't.
Qpoint instruments the agent from the inside out
Qpoint taps directly into the AI agent runtime. No gateways, no sidecars, no SDK integration. A single binary discovers every agent on a machine and captures every action it takes at the source.
The result: your existing ops stack becomes agent-aware. Every event feeds into the SIEM, SOC, and compliance tooling you already operate.
Every action, captured
Every file an agent touches, every tool it invokes, every outbound connection it opens, every binary it spawns. Qpoint hooks into every available surface and raises an event for each one.
File Activity
Every read, write, create, delete, and permission change, tied to the agent that made it.
Tool Calls
Every MCP tool call to or from any agent, with tool name, input parameters, and results.
Network Behavior
Every outbound connection, DNS lookup, and HTTP request, with headers, body, and response. LLM API calls included.
Process Execution
Every shell, subprocess, and worker an agent spawns, with full command-line arguments and exit codes. Sub-agents too.
Use our plugins or write your own
Every policy in Qpoint is a plugin. A plugin can log an action, tag it, rewrite it, or block it: file reads, tool calls, outbound requests, and more. Start with the ones that we ship. Write your own to tailor Qpoint for your business.
Tag every tool call for the audit trail
Attach user, session, and a risk tier to every call an agent makes. Agent related events land in the audit trail with full attribution.
// In a plugin
on_tool_call(call) {
  call.attributes["user.email"]   = whoami();
  call.attributes["session.id"]   = current_session();
  call.attributes["risk.tier"]    = classify(call.tool);
  return call;
}Block read actions for sensitive file types
Prevent agents from opening SSH keys, .env files, and credential stores. The agent gets a standard file-not-found error and moves on.
// In a plugin
on_file_open(path) {
  if (path.starts_with("~/.ssh") ||
      path.contains("/.env")   ||
      path.ends_with("/credentials")) {
    return QCONTROL_FILE_BLOCK_WITH(ENOENT);
  }
  return QCONTROL_PASS;
}Strip secrets from prompts before they leave the endpoint
Catch API keys and tokens in outbound requests and swap them for placeholders. The request proceeds with the secret stripped out.
// In a plugin
on_http_request(req) {
  if (req.host == "api.anthropic.com") {
    req.body = redact_secrets(req.body);
  }
  return req;
}Your ops stack wasn't built for AI agents
Each layer of your stack sees only a fragment of what an agent does; none of them monitors the agent directly.
Monitoring comes first: you can't govern or secure what you can't see.
Seconds, not sprints
Qpoint deploys as a single binary directly on the endpoint. No gateways to route through, no enterprise infrastructure to provision, no SDK integration to schedule.
Install, run, and start seeing every AI agent on the machine — in under a minute.