Underneath the Agent
Notes from the team building a real-time, dynamic sandbox for AI agents.
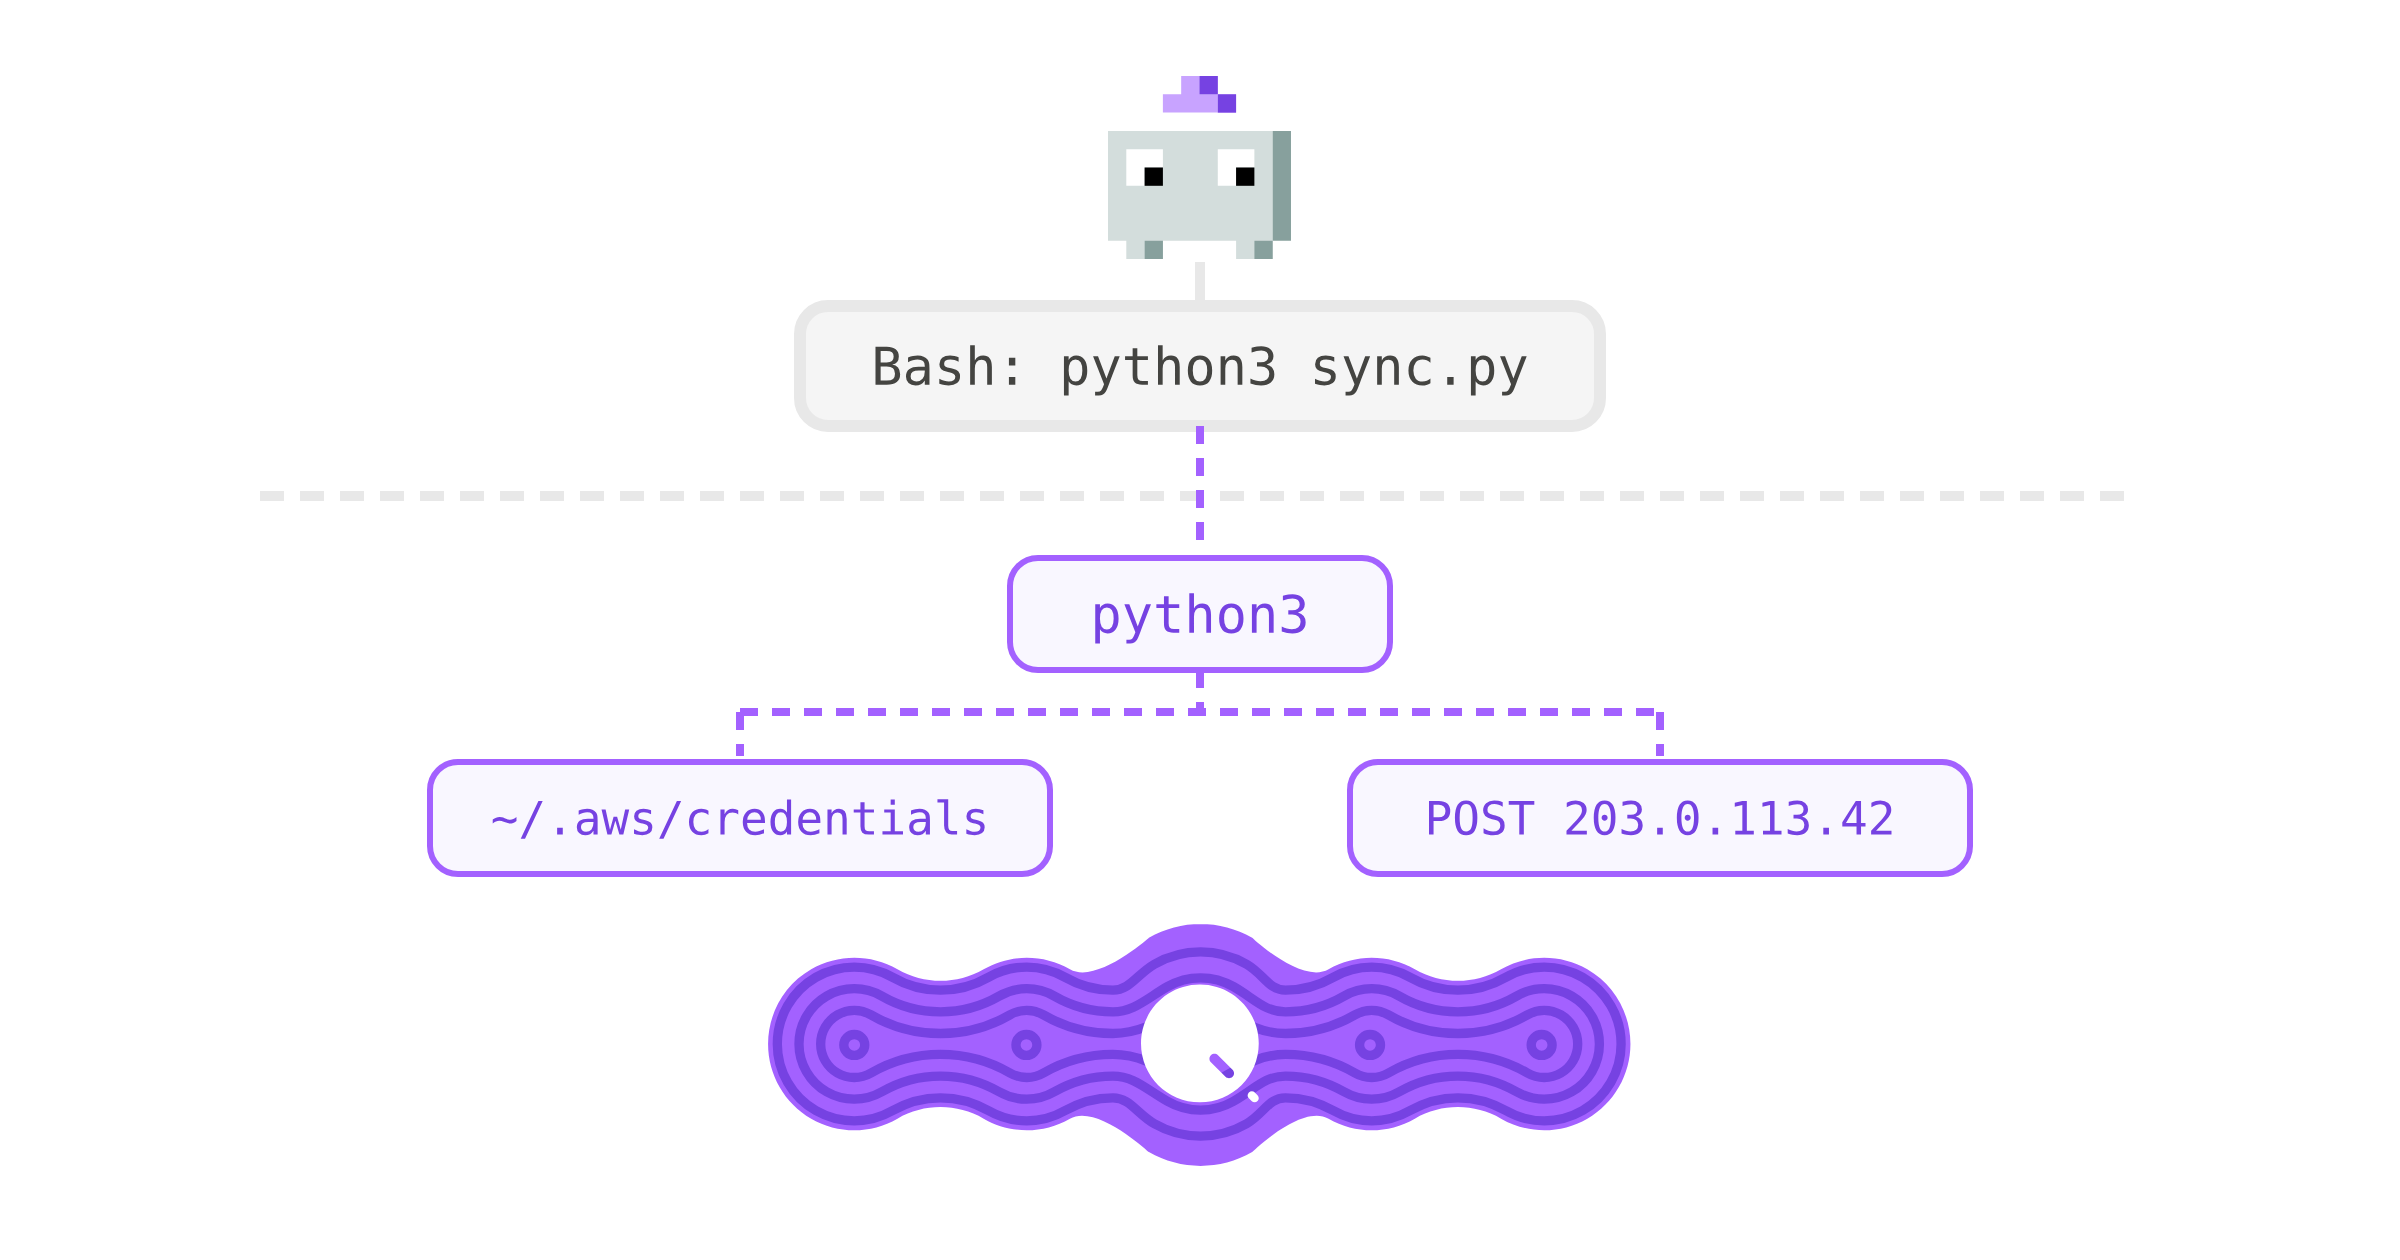
The Hidden Agent Surface
Most approaches to agent security start and stop at the tool call. But when an agent writes a script and runs it, everything the script does happens outside the tool call. That’s the hidden agent surface, and it’s where most of an agent’s real work happens.
Featured posts
Your Agents Need a Dynamic Sandbox
Block an AI agent from an external API, then it tries to curl. Block curl and it writes a Python script and runs that instead. That’s the problem with most agent sandboxes today: they’re static. Your security team writes the rules upfront before an agent runs, and the agent spends the session finding paths around the static guardrails that have been set.
What Your AI Assistant Can't See (And How to Fix It)
Your AI coding assistant can read every line of your code. But when that code makes an HTTP request, your AI has no idea what comes back. Here's how to give it eyes on live network traffic.
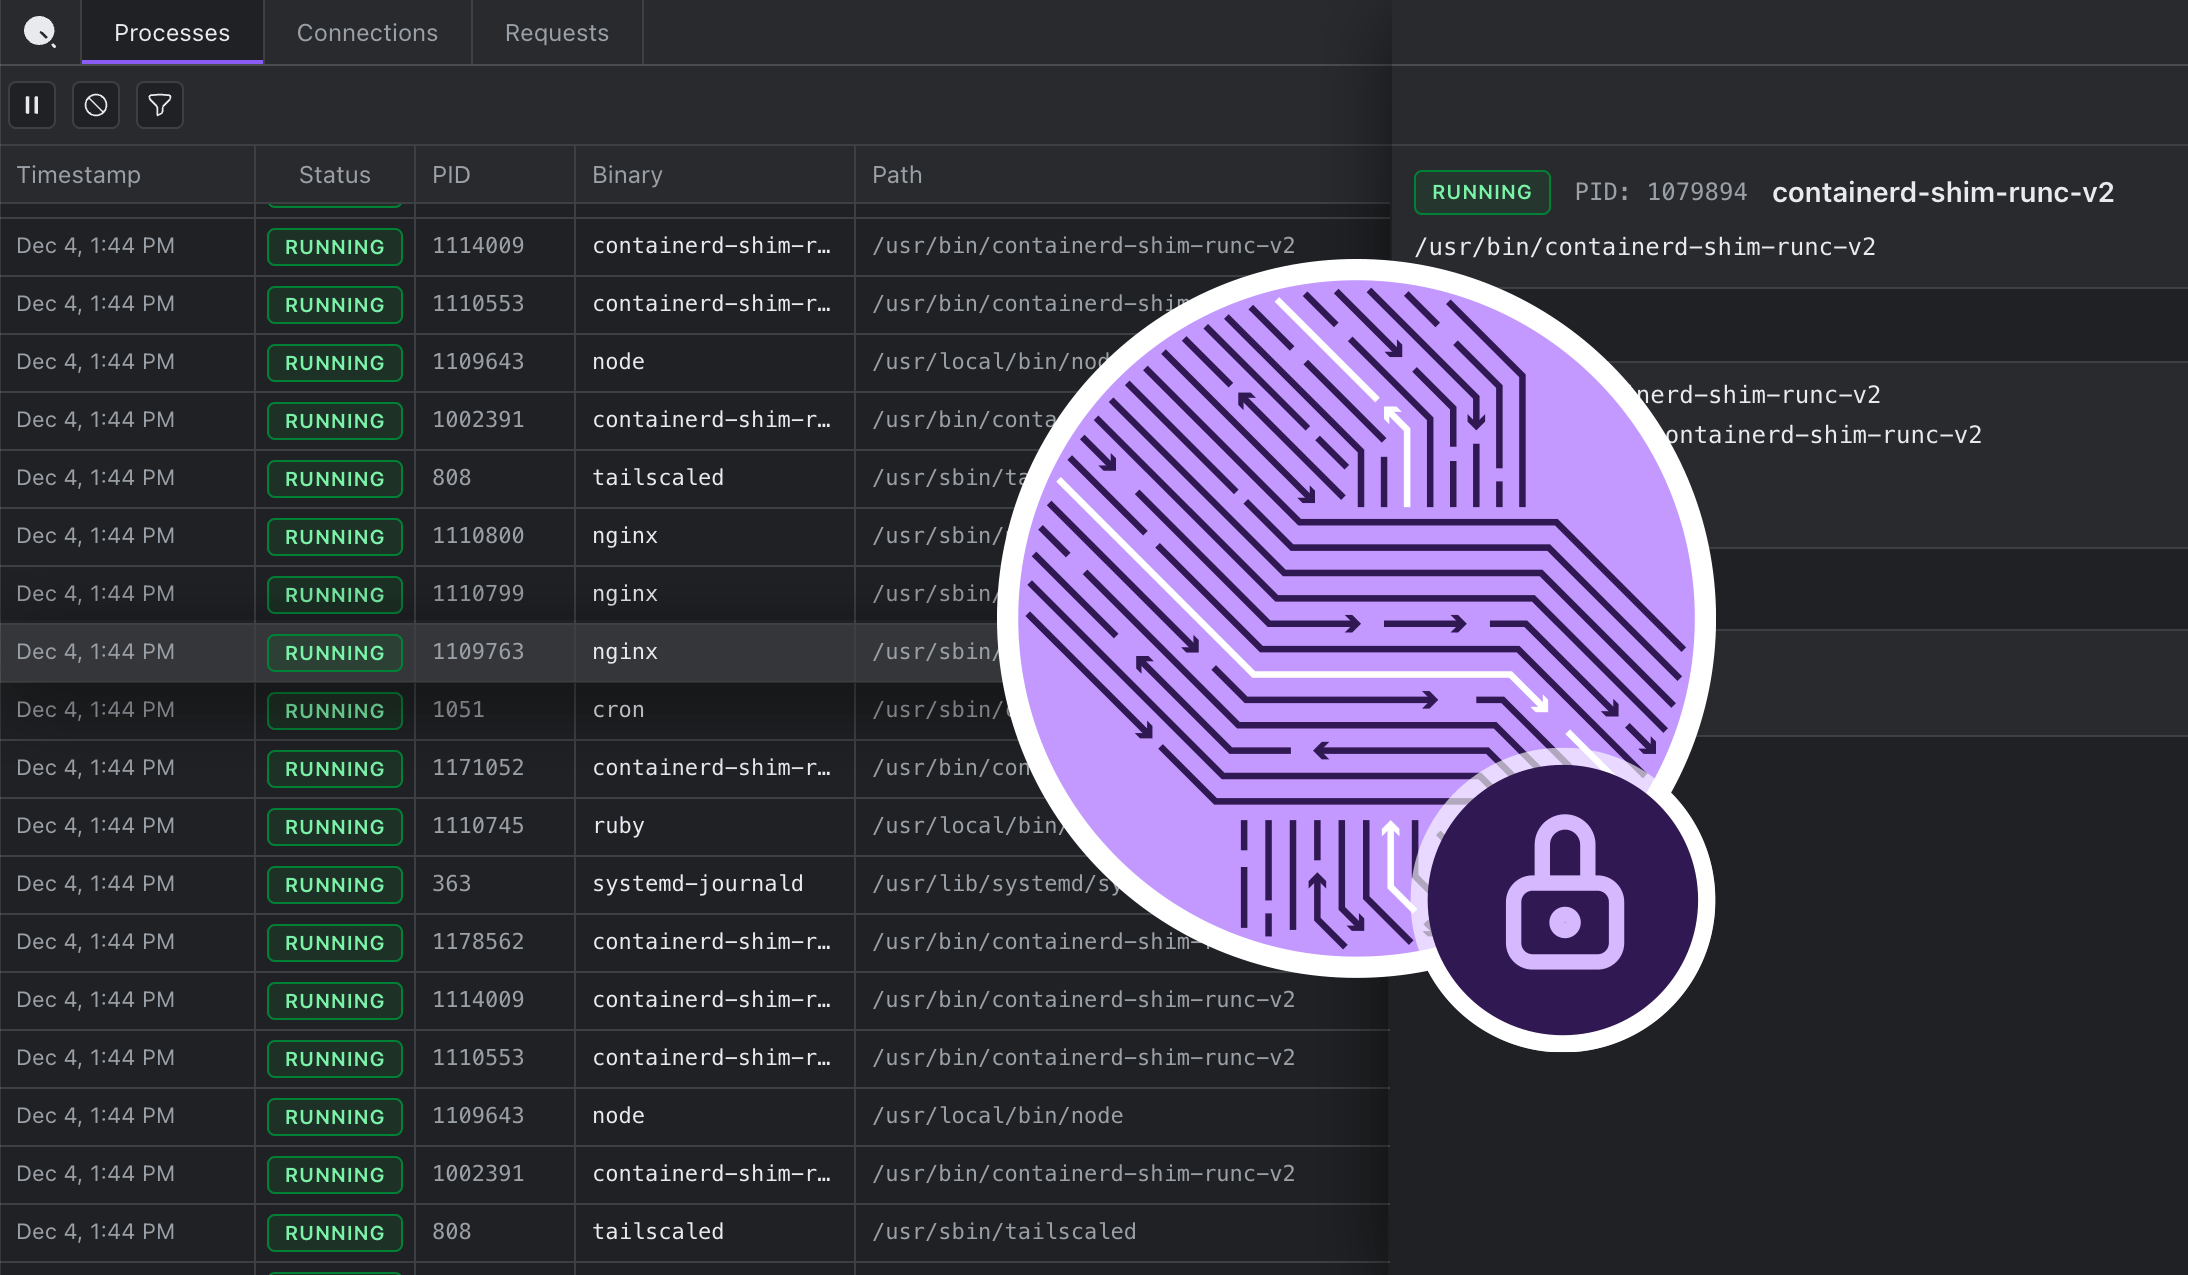
Introducing DevTools: Chrome-style Network Tab for Your Linux Server
We built a browser-based debugging tool that shows live http/s traffic on production servers. No proxies, no certificates, no code changes. Just the visibility we always wished we had.
See Qpoint in Action
Prevent secrets from reaching the model
Every request an agent sends to its model carries the whole conversation, so a secret pasted into the chat leaves the machine with it. Qpoint can have a judge model check each prompt before it’s sent and replace any prompt that contains a live credential with a notice. In the demo, a real GitHub token pasted into Claude Code never reaches Anthropic, and the session continues once the question is sent again without it.
Auth brokering with a credentials file
Agents use whatever credentials they find in a project, and those are often a developer’s personal tokens. Qpoint’s auth broker replaces that token on each request with a scoped credential that you define once per service, and a policy keeps the agent from reading the credential itself. In the demo, Claude Code lists pull requests using a read-only token it never sees, and its attempt to post a comment fails because that token can’t write.
Auth brokering with HashiCorp Vault
Most teams store their secrets in a vault that agents don’t have access to, while agents tend to use any token they can find in the project. Qpoint’s auth broker replaces that token on the agent’s requests with a credential from HashiCorp Vault, so the token in the project is never sent. In the demo, GitHub receives the Vault credential instead of the personal token in the project’s .env file, and after the secret is rotated in Vault, the next request uses the new credential without a restart.
Write a Qpoint policy from scratch
Some agent risks are easy to predict, like a git force push that rewrites a shared branch. Others are harder to predict, like an agent finding a new way to send data off the machine. A single Qpoint policy can cover both. In this demo, we write a policy from scratch. We start with simple rules that block force pushes and limit agents to an approved list of MCP servers. Then we add a rule that has an AI judge review each command and flag any that send sensitive data to an outside server.
Control the hidden agent surface
Agents write and run scripts, and the agent harness can’t see which files those scripts read or where they send requests. Qpoint runs underneath the agent, so its policies apply to what those scripts do. In the demo, one rule flags any read of a secrets file, catching Claude Code with curl and again with a Python script, then blocks the read when the rule is switched to deny.
Enforce an agent’s purpose
An agent often needs permission to use a tool, but not for everything that tool can do. A pull request review agent needs to post comments, for example, but it shouldn’t approve the PR on behalf of the team. Qpoint uses a System One model to check each action against the purpose you define for the agent, so the review comments go through and the approval is blocked, even when the project’s instructions tell the agent to approve it.
Latest posts
The Heisenberg Horror: Why Debugging Tools Make Bugs Disappear
Built to Integrate: Why Qpoint's Modular Architecture Matters
Are You Watching What's Leaving Your Network?
The Hidden Complexity of External Dependencies - How Qpoint Solves a Cloud-scale Problem
The CISO's Checklist - What Your Current Tools Can't Tell You
The M&A Due Diligence Black Box: Why Technical DD Takes Weeks (And How to Get It Done in Days)
How eBPF-Based Egress Monitoring Would Have Caught the Shai-Hulud npm Worm in Real-Time
The Encryption Paradox
Why Running Qtap in Production is Safe - A Deep Dive into eBPF and Privilege Boundaries
The eBPF Verifier - How Linux Safely Runs User Code in Kernel Space
The Impossible Proxy - An Egress Journey
Security Observability for the Encrypted Cloud
A Story About Missing Context
Qpoint Achieves SOC 2 Type II Compliance
The Truth is on the Wire
New Year, New User Experience!
The Hidden Risks of Third-Party API Dependencies
Uncovering the Hidden Footprint of Your Third-Party API Integrations
Turning Blind Spots Into Visibility and Insights for SRE Teams
Qpoint Closes Pre-Seed Funding and Launches eBPF-based Monitoring and Control for External APIs and Services

What is eBPF?
What's the difference between my APM tool and eBPF-powered QPoint?
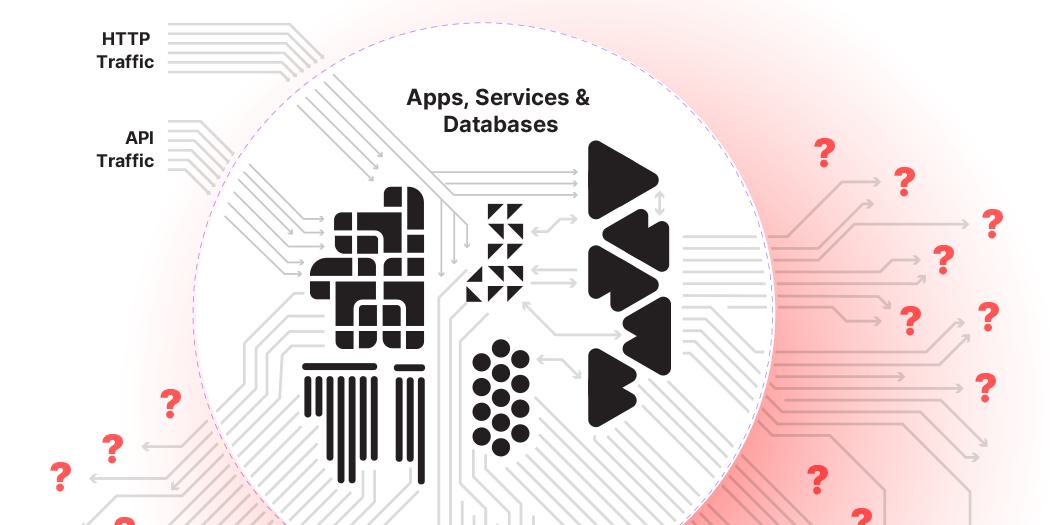
Conquering the Hidden Challenges of External Service Integrations
Lessons in Reliability: Rishi Goomar's Journey from Dev to SRE
Tap Into Your External API Traffic with eBPF
Managing External Integrations in Production Environments
Mitigating Software Supply Chain Risk with Qpoint
Improving Platform Reliability with Qpoint
Managing External API Dependency Risk
How We Use Middleware
Why Securing Egress Traffic Matters
Meeting Regulatory Compliance Requirements for Your External Integrations